×

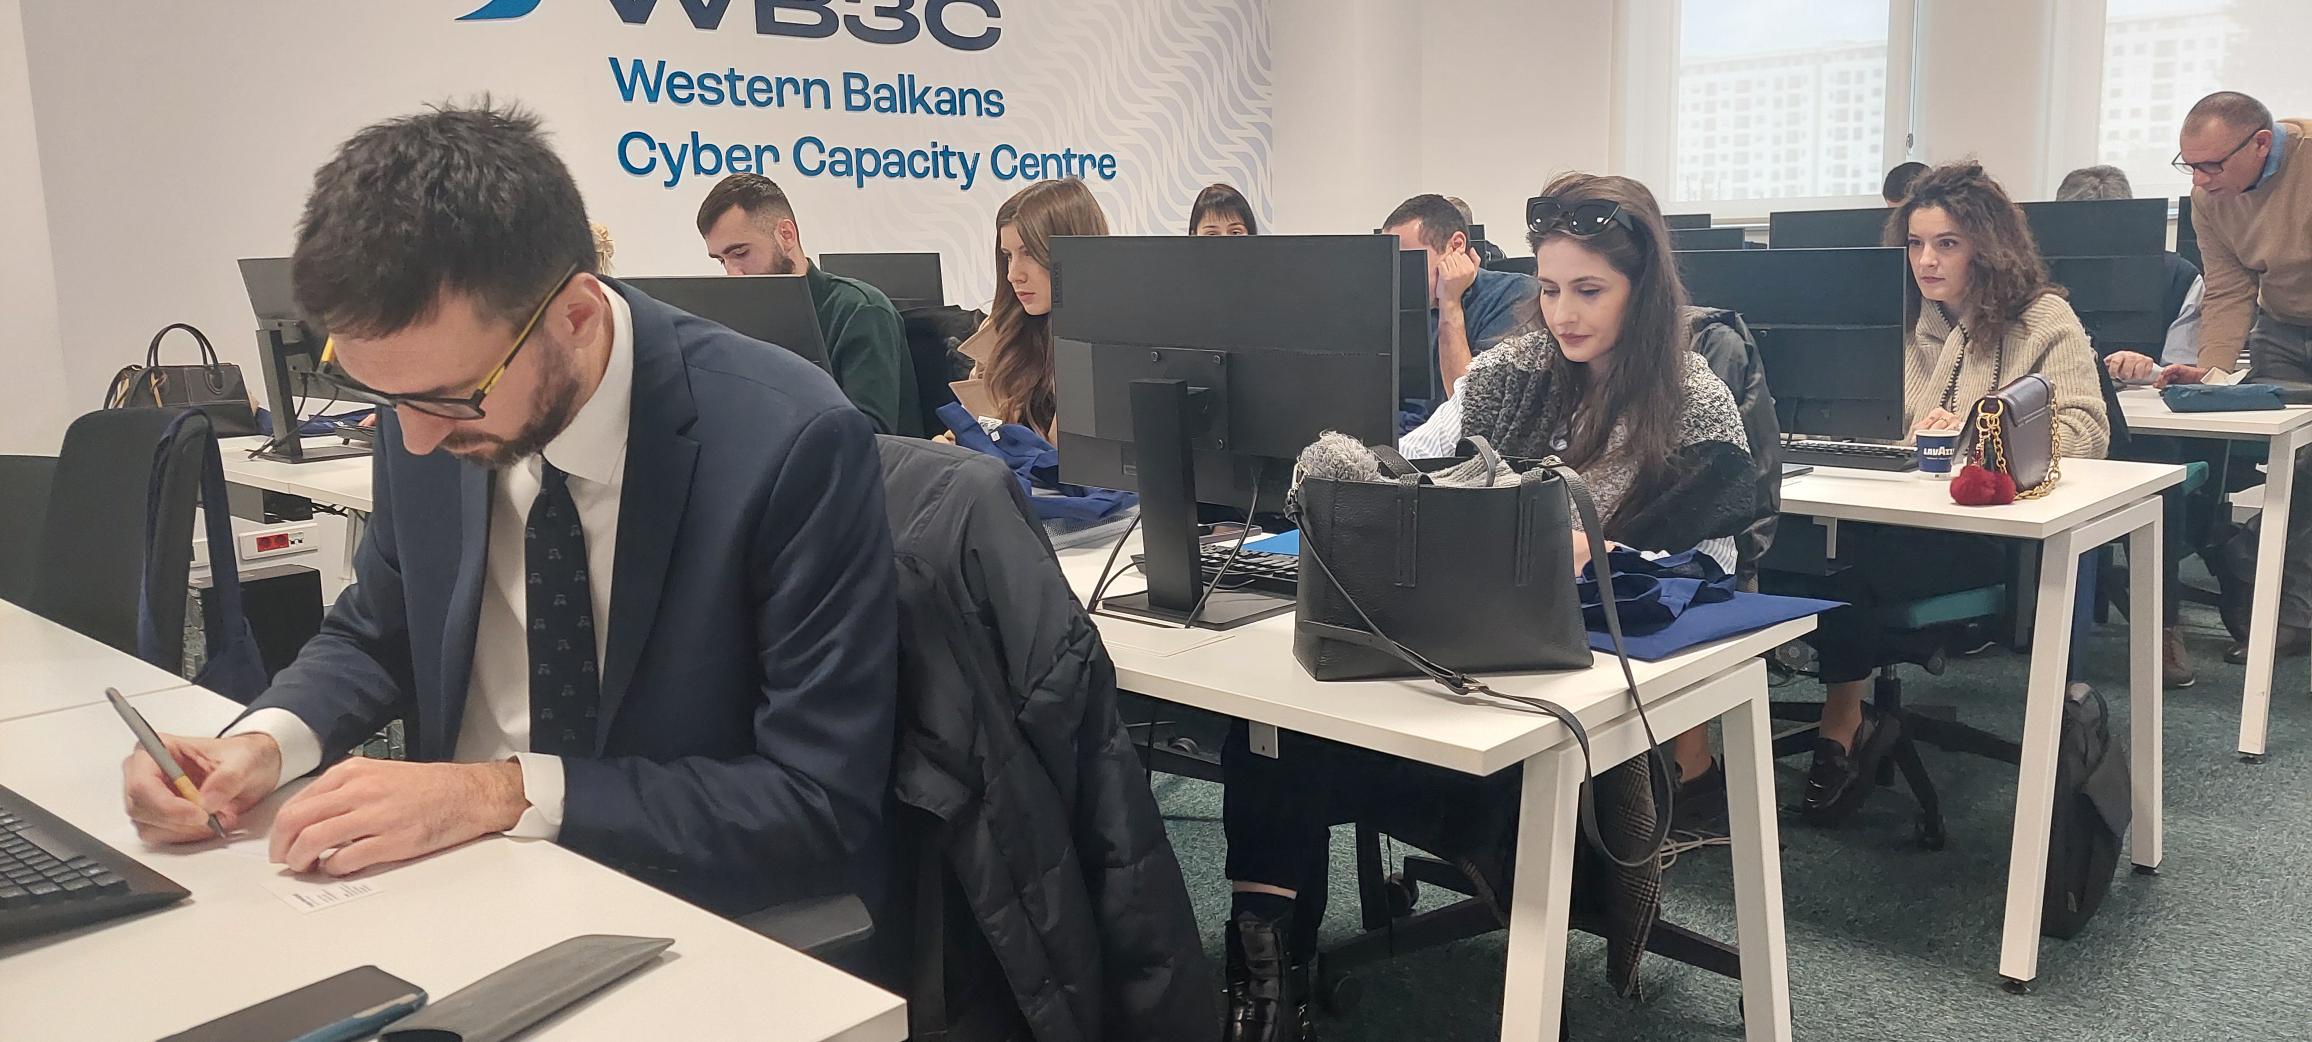
Cyber Hygiene Training for Ministry of European Affairs of Montenegro

28.01.2026

Image for Cyber Hygiene Training for Ministry of European Affairs of Montenegro

Today we start a short CyberHygiene training for colleagues at Montenegro’s Ministry of European Affairs. The training is led by WB3C-s in-house trainers Cyril C. and Yannick Casse.
Over the two days, we will work through the threats civil servants face most often — phishing, malware/ransomware and social engineering — and the practical habits that reduce risk without needing to advance technical skills such as: safer daily practices, data confidentiality and clear incident response basics.
A reminder worth repeating: cyber hygiene is organizational hygiene. Firewalls and policies help, but day-to-day resilience is built in small decisions made across the institution. Every civil servant counts.
A simple checklist that pays off:
⚠️ Pause before you click (especially “urgent” emails)
⚠️ Use strong passwords/passphrases + multi-factor authentication where available
⚠️ Keep devices and apps updated
⚠️ Report suspicious activity early—speed matters

Director Gilles Schwoerer greeted the participants by emphasizing that cybersecurity culture doesn’t start in the IT department, but it starts in each inbox. We are very pleased to welcome the behind-the-scenes force driving Montenegro's successful advancement towards the EU accession and to share that WB3C is expecting its first multi-year EU grant in March this year, aimed at supporting the region in meeting the requirements from the cyber agenda and strengthening its overall resilience, especially its critical infrastructure. We look forward to joining forces with ministries around the region in 2026 - a year expected to bring a dynamic plan of activities.


OSINT and the dark web: supporting anti-drug investigations

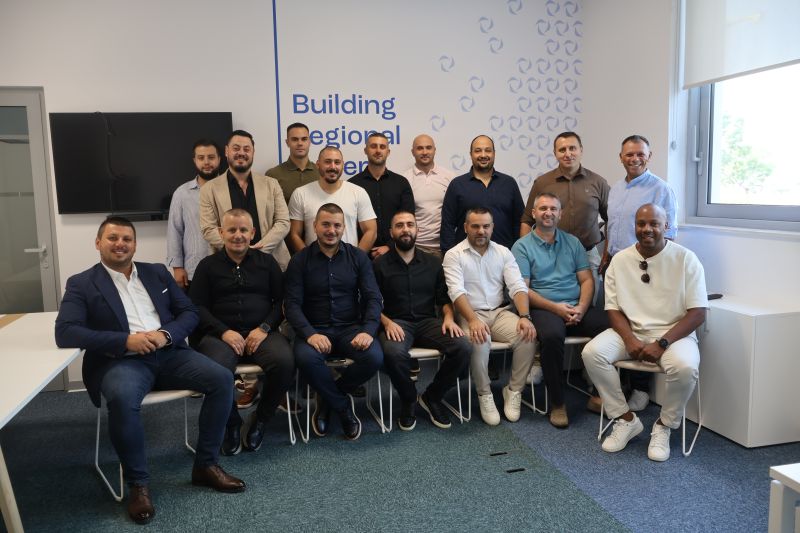
This week at WB3C, we concluded a four-day OSINT – Dark Web training for anti-drug police units, coming from law enforcement units from across the Western Balkans. The course was designed for police officers working in drug units and joining a WB3C training for the first time. 
The focus was practical: how publicly available information can support internet-based investigations, from identifying potential threats and collecting digital evidence to producing actionable intelligence for operational decision-making. 
Over four days, participants worked through the fundamentals of OSINT, evidence preservation, online protection and anonymisation, social-network investigations, investigative checks, the dark web, and structured data-collection planning. Particular attention was given to preserving the integrity of digital evidence and navigating online environments safely and securely. 
The training was delivered by Nicholas Michee from OFAST, France, together with Cyril CORRIAS, WB3C’s cybercrime trainer. Combining specialist anti-drug investigation experience with cybercrime expertise, they guided participants through the technical and investigative aspects of using open-source information and online environments in support of operational work.
Thank you to Nicholas Michee and our partners at OFAST, France, for their cooperation and expertise, and to Cyril Corrias for his contribution to the training. Thank you also to the participating officers for four days of focused practical work and professional exchange.


“We just got hacked!”

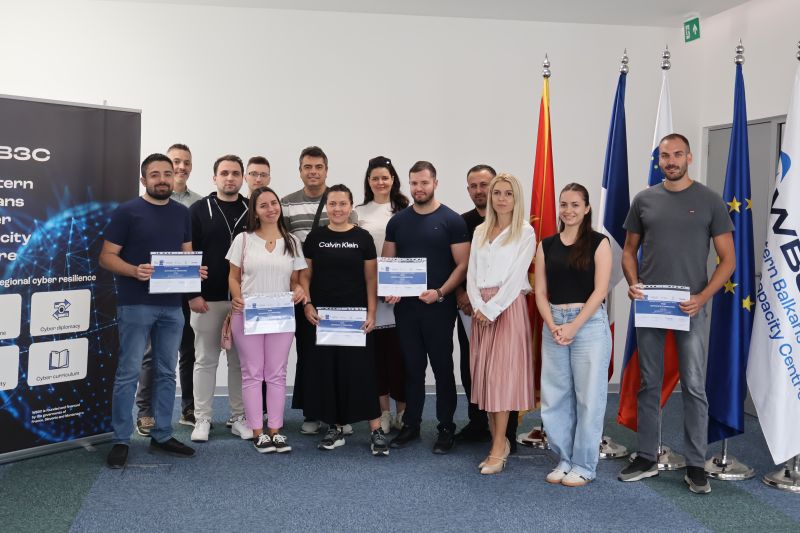
 Yesterday, we wrapped up “We just got hacked”, a basic three-day technical training on incident response for entry level system administrators and cybersecurity specialists from regional public institutions to work through what happens after a security alert becomes a real incident: how to triage it, identify what matters first, analyse logs, trace the likely attack vector and examine suspicious files for indicators of compromise. 

Participants worked with the MITRE ATT&CK framework, connecting investigative findings with attacker tactics and techniques, and looking at how those findings can be translated into practical hardening and preventive measures. The objective was not simply to understand how an incident happened, but to use that analysis to reduce the organisation’s exposure to similar attacks in the future. 
The training was delivered by Jakub Bajera and Krzysztof Chudzik from NASK – Naukowa i Akademicka Sieć Komputerowa / Research and Academic Computer Network, Poland. We also thank our funding partners at URSIV, Urad Vlade Republike Slovenije za informacijsko varnost for their continued support to WB3C and to the development of cybersecurity capacities across the Western Balkans.
Certificates are awarded by Jean-Pierre Bonnet, JP BNT, our new WB3C colleague working across cybercrime and cybersecurity.

WB3C meets critical infrastrucutre operators in Prishtina

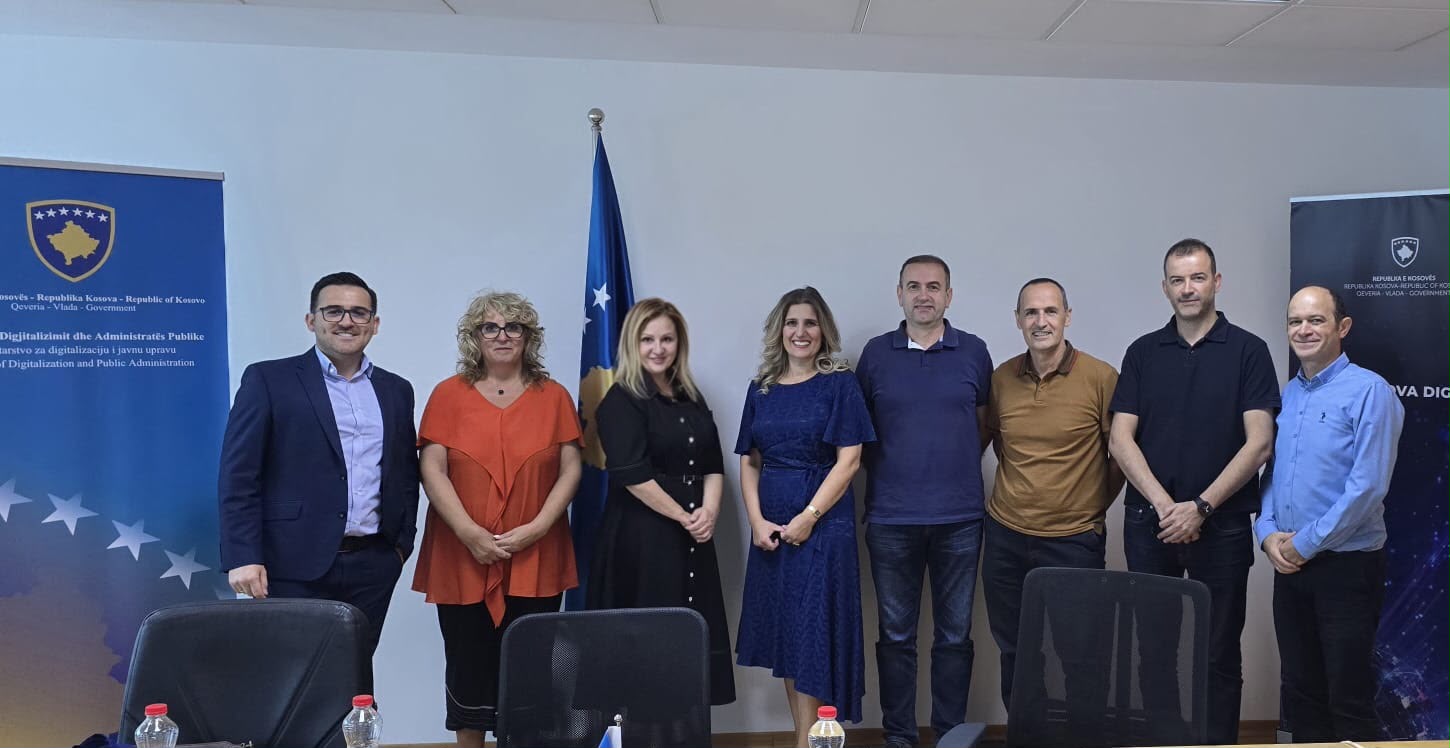
During a recent mission to Prishtina, WB3C joined CIVIPOL colleagues working on a Gap and Needs Assessment related to the protection of critical infrastructure and public spaces.
While the CIVIPOL assessment focused particularly on the institutional and legislative framework, including the role of the Ministry of Interior and alignment with the EU Critical Entities Resilience (CER) Directive, WB3C used the opportunity to engage directly with critical infrastructure operators and better understand their operational needs.
Together with Shkumbin Saneja from the Ministry of Digitalisation and Public Administration, WB3C met representatives from several key sectors: Arijeta Pajaziti Qerimi and Uran Thaci from energy, Adelina Dumani-Hulaj from Prishtina International Airport, Gazmend Gashi from transport/aviation, Arianit Maraj from telecommunications and Arbnor Imeri from the banking sector.
The discussion provided a useful cross-sector view of existing gaps, operational needs and capacity-building priorities. Despite the differences between sectors, a number of common areas of interest emerged.
This forms part of a wider regional process. WB3C will continue meeting key critical infrastructure stakeholders across the Western Balkans to better understand both sector-specific and shared needs, and to use these findings to shape a training and capacity-building plan tailored to the realities operators are facing.
This work is being carried forward in synergy with our partners under the EU-funded CEPS project, linking institutional assessments with the operational perspective of those responsible for running and protecting critical services.


Copyright © WB3C

Disclaimer: Translations of the original content written in English into other languages are AI generated by Weglot.