×

Regulatory Framework for the Protection of Children Online

27.02.2026

Image for Regulatory Framework for the Protection of Children Online

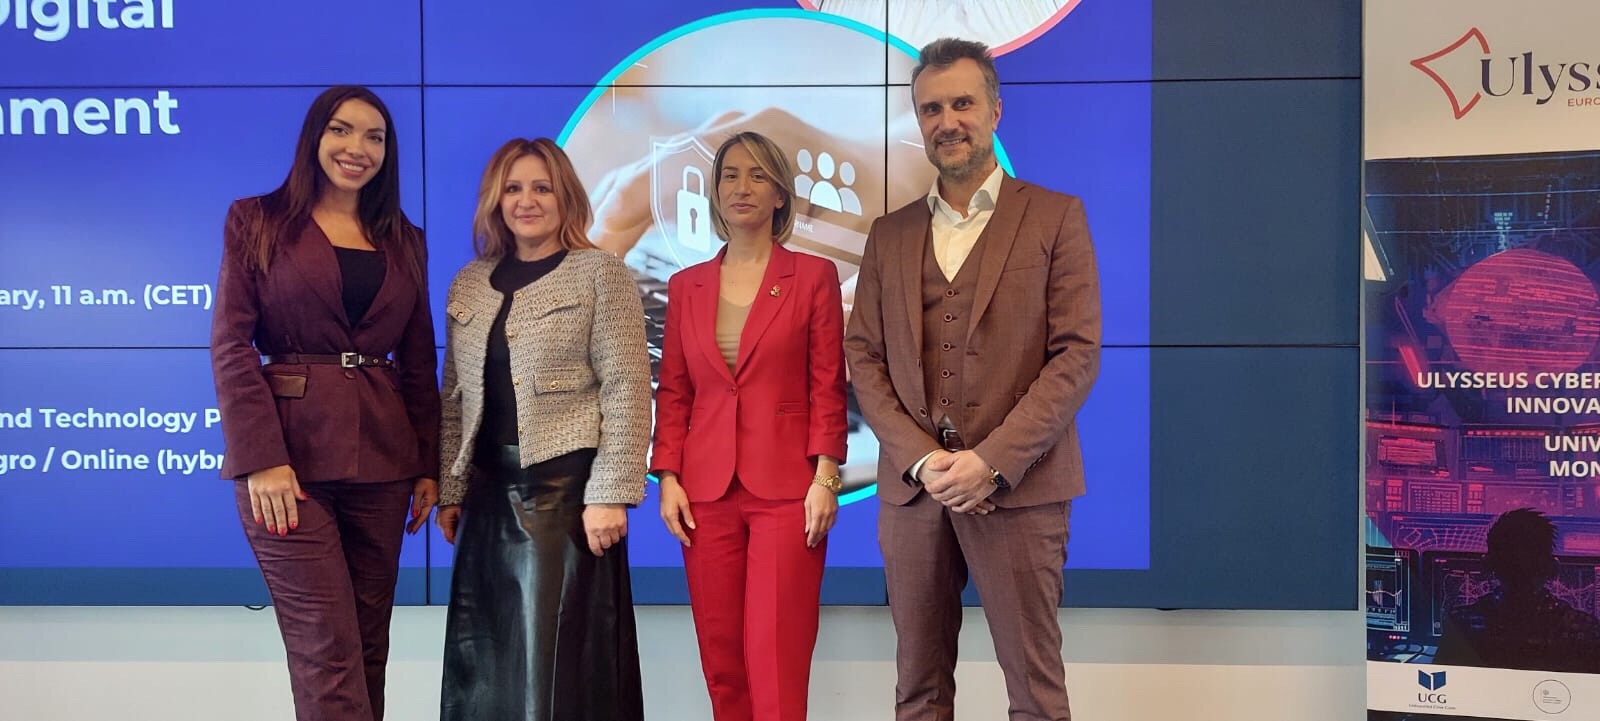
Today, WB3C participated in a multisectoral roundtable on the “Protection of Children in the Digital Environment – A New Draft Law”, hosted by the Ulysseus European University – Innovation Hub for Cybersecurity at the University of Montenegro, led by Andreja Mihailovic, PhD in academic cooperation with the University of Genoa.
The discussion, opened by Prof. Dr. Savo Tomović and MP Slađana Kaludjerović, addressed the proposed Law on the Protection of Minors in the Digital Environment from multiple professional angles.

Our Senior Project Manager Vanja Madzgalj MBE noted that clearly this is an exceptionally complex regulatory space. 
On one hand, states face structural barriers: limited jurisdiction over very large digital platforms operating across borders, difficulties in enforcing obligations against global service providers and the technical opacity of algorithmic systems. On the other hand, children are digital natives with legitimate rights to access, participate in, and benefit from the digital world. Protection cannot mean exclusion.

⚡ At the same time, the data are stark.
We see increasing numbers of minors falling victim to digital crimes, including online sexual exploitation and abuse. We also see minors committing digital offences, often without understanding the legal consequences. Internet addiction is emerging at an early age, with long-term psychological and social impacts. Uncontrolled and unsupervised digital exposure is producing measurable harm.
The forum brought together ICT professionals, children’s rights organizations, parent associations, regulators, policymakers, and educators. 

There was broad agreement that:
Cross-border cooperation with EU regulators is essential, particularly in light of the Digital Services Act and emerging European enforcement mechanisms.
Parents and schools carry a critical share of responsibility.
Children’s rights — including access to information and digital participation — must be preserved alongside protection measures.
Clear criminalization of digital child sexual abuse material (CSAM), grooming, and manipulation of minors online is essential.
We also agreed that waiting for perfect solutions is not an option. We must start somewhere.
National awareness campaigns on digital risks, structured parental education, and early cybersecurity education in schools are foundational. Parents need greater support — and greater accountability. At the same time, targeted institutional regulation and enforceable legal provisions remain necessary, particularly in areas of exploitation, manipulation, and platform responsibility.
Protecting minors online is not a single-law issue. It is a societal, institutional, and technological challenge that requires coordinated national action and effective alignment with European regulatory frameworks. The complexity should not paralyze us — it should push us toward pragmatic, enforceable, and balanced solutions.


OSINT and the dark web: supporting anti-drug investigations

This week at WB3C, we concluded a four-day OSINT – Dark Web training for anti-drug police units, coming from law enforcement units from across the Western Balkans. The course was designed for police officers working in drug units and joining a WB3C training for the first time. 
The focus was practical: how publicly available information can support internet-based investigations, from identifying potential threats and collecting digital evidence to producing actionable intelligence for operational decision-making. 
Over four days, participants worked through the fundamentals of OSINT, evidence preservation, online protection and anonymisation, social-network investigations, investigative checks, the dark web, and structured data-collection planning. Particular attention was given to preserving the integrity of digital evidence and navigating online environments safely and securely. 
The training was delivered by Nicholas Michee from OFAST, France, together with Cyril CORRIAS, WB3C’s cybercrime trainer. Combining specialist anti-drug investigation experience with cybercrime expertise, they guided participants through the technical and investigative aspects of using open-source information and online environments in support of operational work.
Thank you to Nicholas Michee and our partners at OFAST, France, for their cooperation and expertise, and to Cyril Corrias for his contribution to the training. Thank you also to the participating officers for four days of focused practical work and professional exchange.


“We just got hacked!”

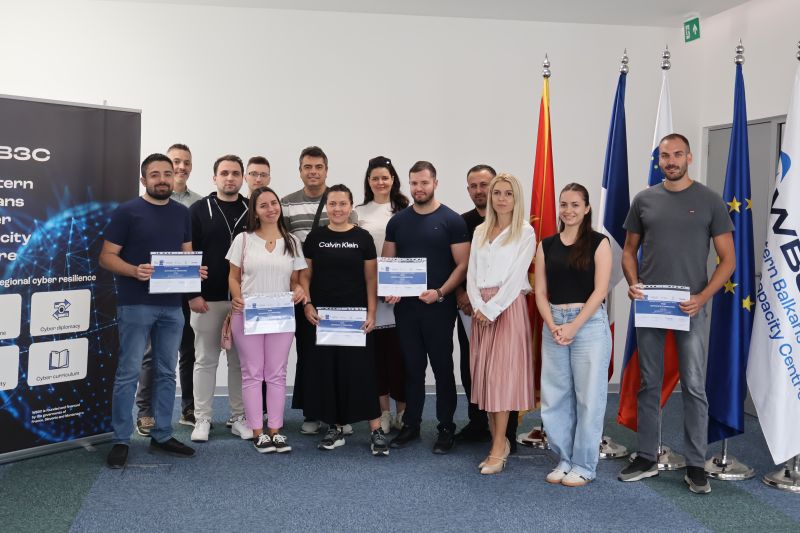
 Yesterday, we wrapped up “We just got hacked”, a basic three-day technical training on incident response for entry level system administrators and cybersecurity specialists from regional public institutions to work through what happens after a security alert becomes a real incident: how to triage it, identify what matters first, analyse logs, trace the likely attack vector and examine suspicious files for indicators of compromise. 

Participants worked with the MITRE ATT&CK framework, connecting investigative findings with attacker tactics and techniques, and looking at how those findings can be translated into practical hardening and preventive measures. The objective was not simply to understand how an incident happened, but to use that analysis to reduce the organisation’s exposure to similar attacks in the future. 
The training was delivered by Jakub Bajera and Krzysztof Chudzik from NASK – Naukowa i Akademicka Sieć Komputerowa / Research and Academic Computer Network, Poland. We also thank our funding partners at URSIV, Urad Vlade Republike Slovenije za informacijsko varnost for their continued support to WB3C and to the development of cybersecurity capacities across the Western Balkans.
Certificates are awarded by Jean-Pierre Bonnet, JP BNT, our new WB3C colleague working across cybercrime and cybersecurity.

WB3C meets critical infrastrucutre operators in Prishtina

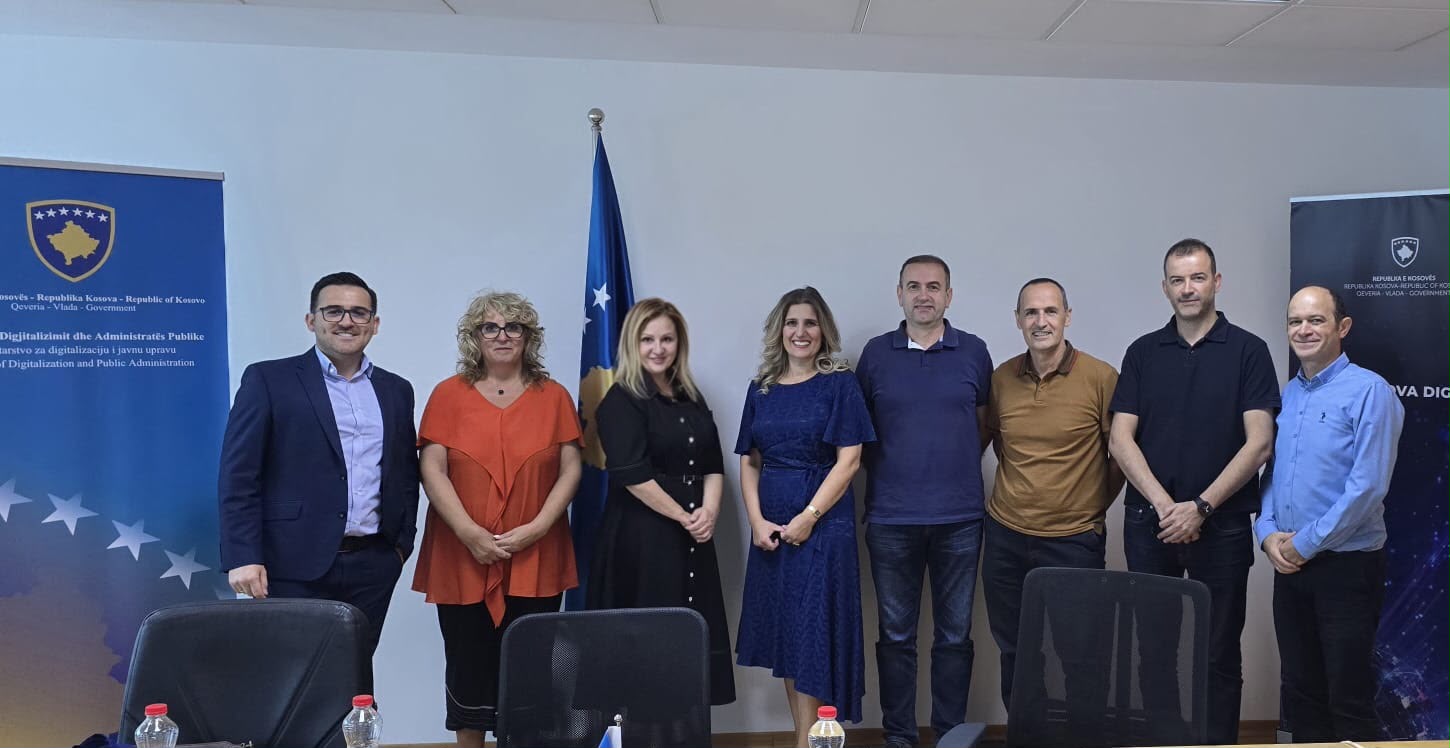
During a recent mission to Prishtina, WB3C joined CIVIPOL colleagues working on a Gap and Needs Assessment related to the protection of critical infrastructure and public spaces.
While the CIVIPOL assessment focused particularly on the institutional and legislative framework, including the role of the Ministry of Interior and alignment with the EU Critical Entities Resilience (CER) Directive, WB3C used the opportunity to engage directly with critical infrastructure operators and better understand their operational needs.
Together with Shkumbin Saneja from the Ministry of Digitalisation and Public Administration, WB3C met representatives from several key sectors: Arijeta Pajaziti Qerimi and Uran Thaci from energy, Adelina Dumani-Hulaj from Prishtina International Airport, Gazmend Gashi from transport/aviation, Arianit Maraj from telecommunications and Arbnor Imeri from the banking sector.
The discussion provided a useful cross-sector view of existing gaps, operational needs and capacity-building priorities. Despite the differences between sectors, a number of common areas of interest emerged.
This forms part of a wider regional process. WB3C will continue meeting key critical infrastructure stakeholders across the Western Balkans to better understand both sector-specific and shared needs, and to use these findings to shape a training and capacity-building plan tailored to the realities operators are facing.
This work is being carried forward in synergy with our partners under the EU-funded CEPS project, linking institutional assessments with the operational perspective of those responsible for running and protecting critical services.


Copyright © WB3C

Disclaimer: Translations of the original content written in English into other languages are AI generated by Weglot.