×

RCC CyberPulse 2025: Regional Stakeholder Join Forces in Cybersecurity

02.07.2025

Image for RCC CyberPulse 2025: Regional Stakeholder Join Forces in Cybersecurity

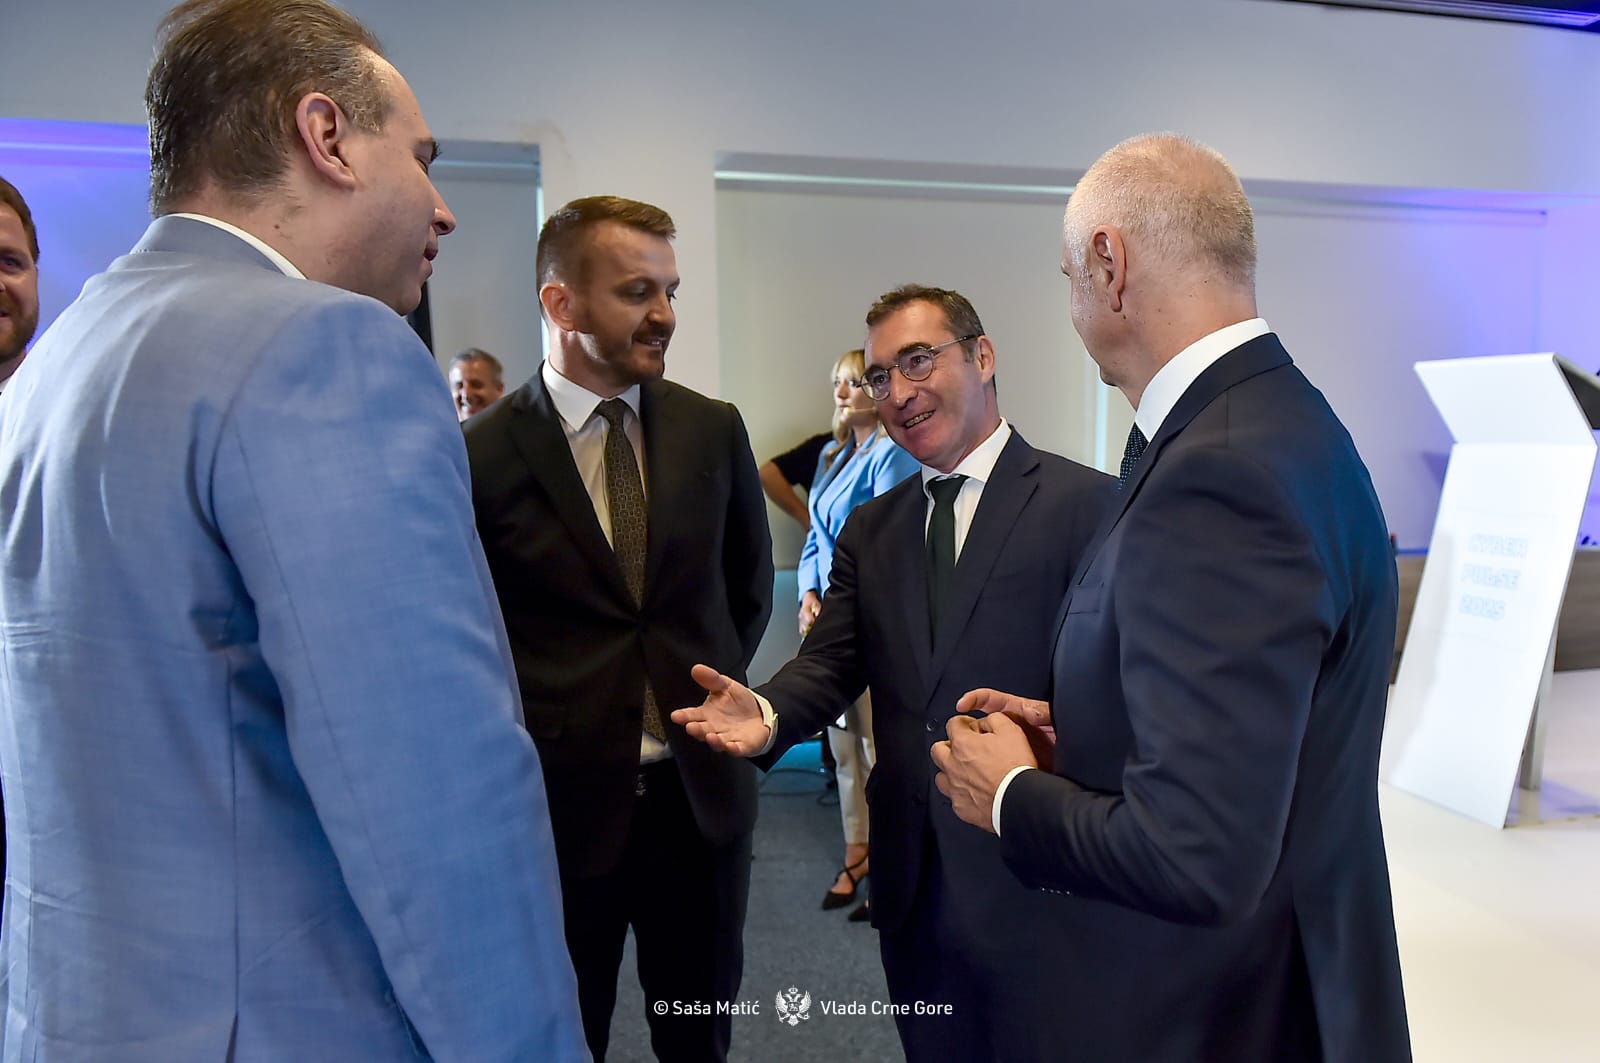
The High-Level Western Balkans Cybersecurity Conference – CyberPulse 2025: Tracking Progress, Building Resilience, Driving Change – gathered government representatives, EU institutions, regional organizations, cybersecurity experts and private sector leaders to address the growing cyber threat landscape in the Western Balkans.

CyberPulse 2025 focused on three priorities:

  • addressing current gaps in regional cyber capacities,
  • exploring the role of emerging technologies, and
  • operationalising joint initiatives and partnerships.

Opening Remarks

The conference opened with high-level messages of commitment to regional cyber resilience:

  • Amer Kapetanović, Secretary General of the RCC, highlighted the sharp rise in cyber incidents and stressed that trust, political will and coordinated regional action are the strongest “firewall” against threats. He also announced the development of the new regional cybersecurity needs database.
  • Filip Ivanović, Deputy Prime Minister of Montenegro for Foreign and European Affairs, emphasized Montenegro’s adoption of European cybersecurity standards and its vision of a secure, resilient digital future as part of EU integration.
  • Michael Docherty, speaking on behalf of the European Commission Delegation, reaffirmed EU support for the region through initiatives with ENISA and the Council of Europe, underlining that cybersecurity is now a central element of the EU Growth Plan for the Western Balkans.
  • Gilles Schwoerer, Head of WB3C, noted that while digital transformation offers many opportunities, it also expands the attack surface, underscoring the urgent need for secure digital pathways and collective resilience.

Conference Panels

  • High-Level Panel: Stronger Connectivity, Smarter Security, Resilient Future (moderated by Danijela Gačević, Head of the Programme Department, RCC)
    Senior government representatives from the region exchanged views on national priorities, institutional capacities, and EU integration in the field of cybersecurity.
    • Governments stressed the shortage of cybersecurity professionals as a critical challenge.
    • Kosovo*’s representative emphasized dependence on external consultants and the need to train public servants internally.
    • Montenegro focused on intersectoral cooperation and the role of NATO and EU support.
    • North Macedonia presented its new Ministry for Digital Transformation and its national cybersecurity strategy.

      Panelists:

    • Bardhyl Dobra – Deputy Minister of Internal Affairs, Pristina
    • Naim Gjokaj – State Secretary, Ministry of Public Administration, Podgorica
    • Radoslav Nastasijevikj Vardjiski – Deputy Minister for Digital Transformation, Skopje


  • Navigating Cyber Threats in the Western Balkans: The Evolving Role of AI and Emerging Technologies (moderated by Mirza Jamaković, Prosecutor's Office Sarajevo)
    Experts from Europol, law enforcement, and the private sector discussed the opportunities and risks of AI, from forensic tools to the misuse of generative AI by organized crime groups.
    • Europol described using machine learning to analyze millions of data points in criminal investigations.
    • Concerns raised about organized crime groups developing their own AI tools, including large language models, for cybercrime.
    • Calls for explainable and transparent AI outcomes in cybersecurity decision-making.
    • Oracle warned against uploading confidential data into public AI tools, stressing regulatory gaps.

      Panelists:

    • Emmanuel Kessler – Europol
    • Jelena Zelenović Matone – WomenCyberForce / Women4Cyber
    • Nenad Bogunović – Cybercrime Unit, Belgrade
    • Amar Dedović – Oracle


  • Empowering Talent: Skill-Building for the Future in the Western Balkans (moderated by Andreja Mihailović, Women4Cyber Montenegro)
    The session focused on education, workforce shortages, women’s participation in cybersecurity, and ways to redirect youth talent from informal digital activities to formal opportunities.
    • Highlighted that women’s participation in cybersecurity remains below 20% in the Western Balkans.
    • Croatia shared progress from 30% to 52% female participation in the UN Cybersecurity Working Group between 2019 and 2024.
    • Albania’s Cybersecurity Agency argued for education reform starting at primary school.
    • Open Society Foundation raised concerns about youth involvement in grey/illegal digital activities, calling for redirection into formal sectors.

      Panelists:

    • Tamara Tafra – Deputy Minister of Foreign and European Affairs, Zagreb
    • Igli Tafa – Director, National Cybersecurity Agency, Tirana
    • Andi Dobrushi – Open Society Foundation
    • Fabio di Franco – ENISA


  • Integrating Experience and Strategy: A Multisector Dialogue on SOC Advancement (moderated by Vanja Madžgalj, WB3C)
    Panelists shared good practices for building and operating Security Operations Centres, stressing the importance of policy alignment, inter-sectoral cooperation and trust-building between public and private actors.
  • Albania’s national experience showed that the 2022 cyberattack became a catalyst for building SOC capacity and adopting “zero trust” and defense-in-depth strategies.
  • Differences between public and private sector approaches to threat intelligence were emphasized, with trust and data-sharing seen as barriers for public institutions.
  • North Macedonia introduced a new law placing the Ministry for Digital Transformation as the central cybersecurity authority.

    Panelists:

    • Franc Zyliftari – Head of Incident Response Team, Tirana
    • Philippe Gillet – Gatewatcher, Paris
    • Aleksandar Acev – Cyber Balkans, Skopje


  • Sectors United Against Cyber Threats: Building Bridges Across Sectors (Milan Sekuloski, e-Governance Academy, Tallinn)
    This discussion brought together public institutions, civil society, academia, and the private sector, highlighting how multi-stakeholder collaboration is essential to strengthening regional resilience.
    • Pristina shared good practices in bringing all relevant actors together regularly on critical infrastructure protection.
    • Civil society organizations were recognized as important but vulnerable actors requiring targeted cyber hygiene tools and support.
    • SMEs were highlighted as particularly exposed, requiring systemic support from the public sector.
    • The EBRD linked its investment strategy to cybersecurity, showing that infrastructure projects cannot be sustainable without integrated cyber risk management.

      Panelists:

    • Lulezon Jagxhiu – Prime Minister’s Cabinet, Pristina
    • Predrag Puharić – Cybersecurity Centre of Excellence, Sarajevo
    • Ivona Dabetić – NGO Secure, Podgorica
    • Roy Yarom – European Bank for Reconstruction and Development (EBRD)

The conference concluded that cybersecurity in the Western Balkans can no longer be treated as a purely technical issue but must be recognized as a strategic priority, requiring long-term cooperation, sustained investment and coordinated regional action.


OSINT and the dark web: supporting anti-drug investigations

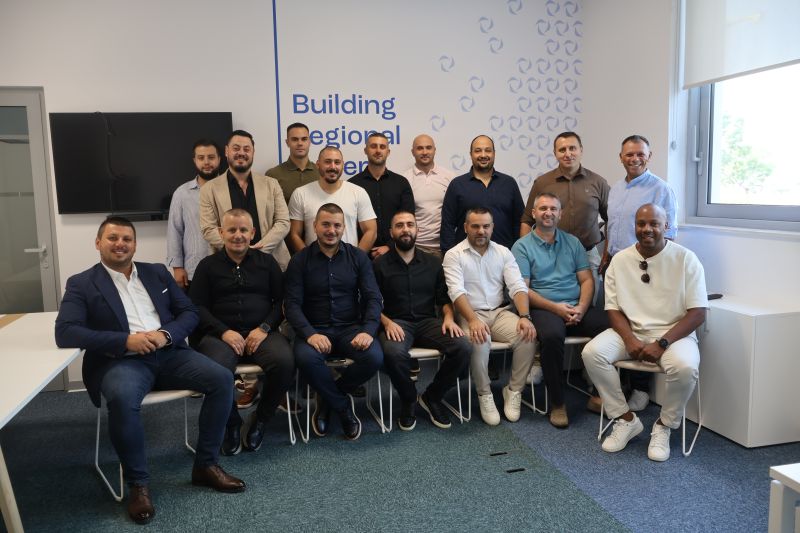
This week at WB3C, we concluded a four-day OSINT – Dark Web training for anti-drug police units, coming from law enforcement units from across the Western Balkans. The course was designed for police officers working in drug units and joining a WB3C training for the first time. 
The focus was practical: how publicly available information can support internet-based investigations, from identifying potential threats and collecting digital evidence to producing actionable intelligence for operational decision-making. 
Over four days, participants worked through the fundamentals of OSINT, evidence preservation, online protection and anonymisation, social-network investigations, investigative checks, the dark web, and structured data-collection planning. Particular attention was given to preserving the integrity of digital evidence and navigating online environments safely and securely. 
The training was delivered by Nicholas Michee from OFAST, France, together with Cyril CORRIAS, WB3C’s cybercrime trainer. Combining specialist anti-drug investigation experience with cybercrime expertise, they guided participants through the technical and investigative aspects of using open-source information and online environments in support of operational work.
Thank you to Nicholas Michee and our partners at OFAST, France, for their cooperation and expertise, and to Cyril Corrias for his contribution to the training. Thank you also to the participating officers for four days of focused practical work and professional exchange.


“We just got hacked!”

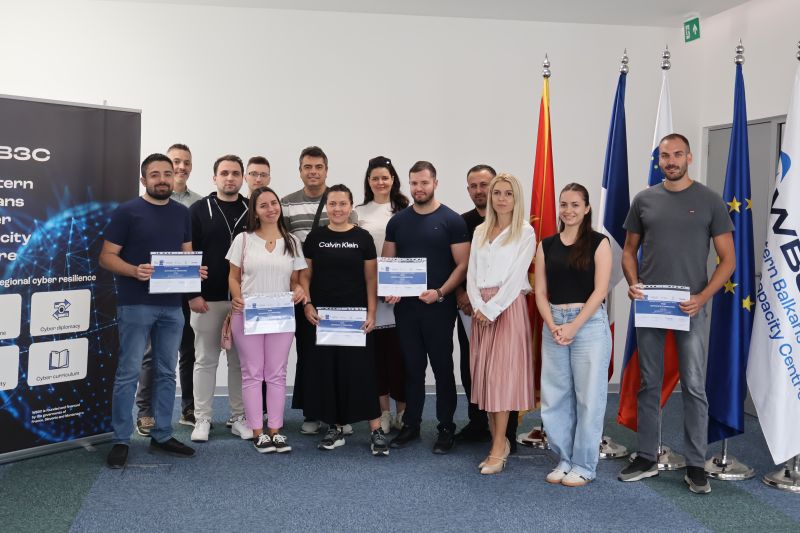
 Yesterday, we wrapped up “We just got hacked”, a basic three-day technical training on incident response for entry level system administrators and cybersecurity specialists from regional public institutions to work through what happens after a security alert becomes a real incident: how to triage it, identify what matters first, analyse logs, trace the likely attack vector and examine suspicious files for indicators of compromise. 

Participants worked with the MITRE ATT&CK framework, connecting investigative findings with attacker tactics and techniques, and looking at how those findings can be translated into practical hardening and preventive measures. The objective was not simply to understand how an incident happened, but to use that analysis to reduce the organisation’s exposure to similar attacks in the future. 
The training was delivered by Jakub Bajera and Krzysztof Chudzik from NASK – Naukowa i Akademicka Sieć Komputerowa / Research and Academic Computer Network, Poland. We also thank our funding partners at URSIV, Urad Vlade Republike Slovenije za informacijsko varnost for their continued support to WB3C and to the development of cybersecurity capacities across the Western Balkans.
Certificates are awarded by Jean-Pierre Bonnet, JP BNT, our new WB3C colleague working across cybercrime and cybersecurity.

WB3C meets critical infrastrucutre operators in Prishtina

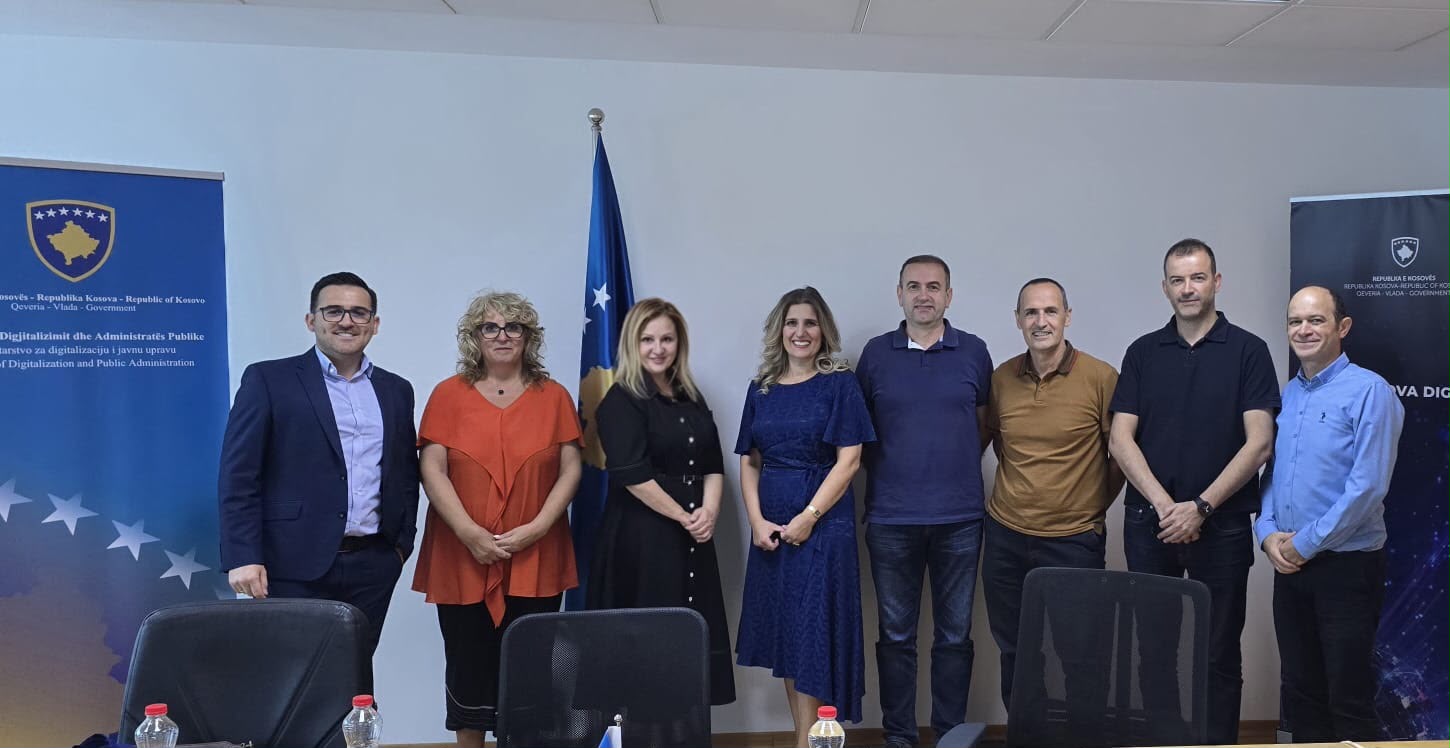
During a recent mission to Prishtina, WB3C joined CIVIPOL colleagues working on a Gap and Needs Assessment related to the protection of critical infrastructure and public spaces.
While the CIVIPOL assessment focused particularly on the institutional and legislative framework, including the role of the Ministry of Interior and alignment with the EU Critical Entities Resilience (CER) Directive, WB3C used the opportunity to engage directly with critical infrastructure operators and better understand their operational needs.
Together with Shkumbin Saneja from the Ministry of Digitalisation and Public Administration, WB3C met representatives from several key sectors: Arijeta Pajaziti Qerimi and Uran Thaci from energy, Adelina Dumani-Hulaj from Prishtina International Airport, Gazmend Gashi from transport/aviation, Arianit Maraj from telecommunications and Arbnor Imeri from the banking sector.
The discussion provided a useful cross-sector view of existing gaps, operational needs and capacity-building priorities. Despite the differences between sectors, a number of common areas of interest emerged.
This forms part of a wider regional process. WB3C will continue meeting key critical infrastructure stakeholders across the Western Balkans to better understand both sector-specific and shared needs, and to use these findings to shape a training and capacity-building plan tailored to the realities operators are facing.
This work is being carried forward in synergy with our partners under the EU-funded CEPS project, linking institutional assessments with the operational perspective of those responsible for running and protecting critical services.


Copyright © WB3C

Disclaimer: Translations of the original content written in English into other languages are AI generated by Weglot.