15.09.2026
Welcoming Étienne David to WB3C!
We are pleased to welcome Étienne David, a master’s student in international relations and war studies at ICES – Catholic University of Vendée (France), who has joined the Western Balkans Cyber Capacity Building Center (WB3C) for a three-month internship (under an internship agreement with the Science and Technology Park of Montenegro).
From September through December 2026, Étienne will gain practical experience within an international organization by supporting the WB3C’s activities in the areas of cybersecurity, cybercrime, and cyberdiplomacy, while familiarizing himself with regional cooperation and security challenges in the Western Balkans.
We are delighted to welcome him, just as we did with Tom Husson (April–July 2026). We wish him an enriching and fruitful experience in Podgorica!
15.09.2026
Cyber awareness, disinformation and OSINT: three connected perspectives on working safely with information
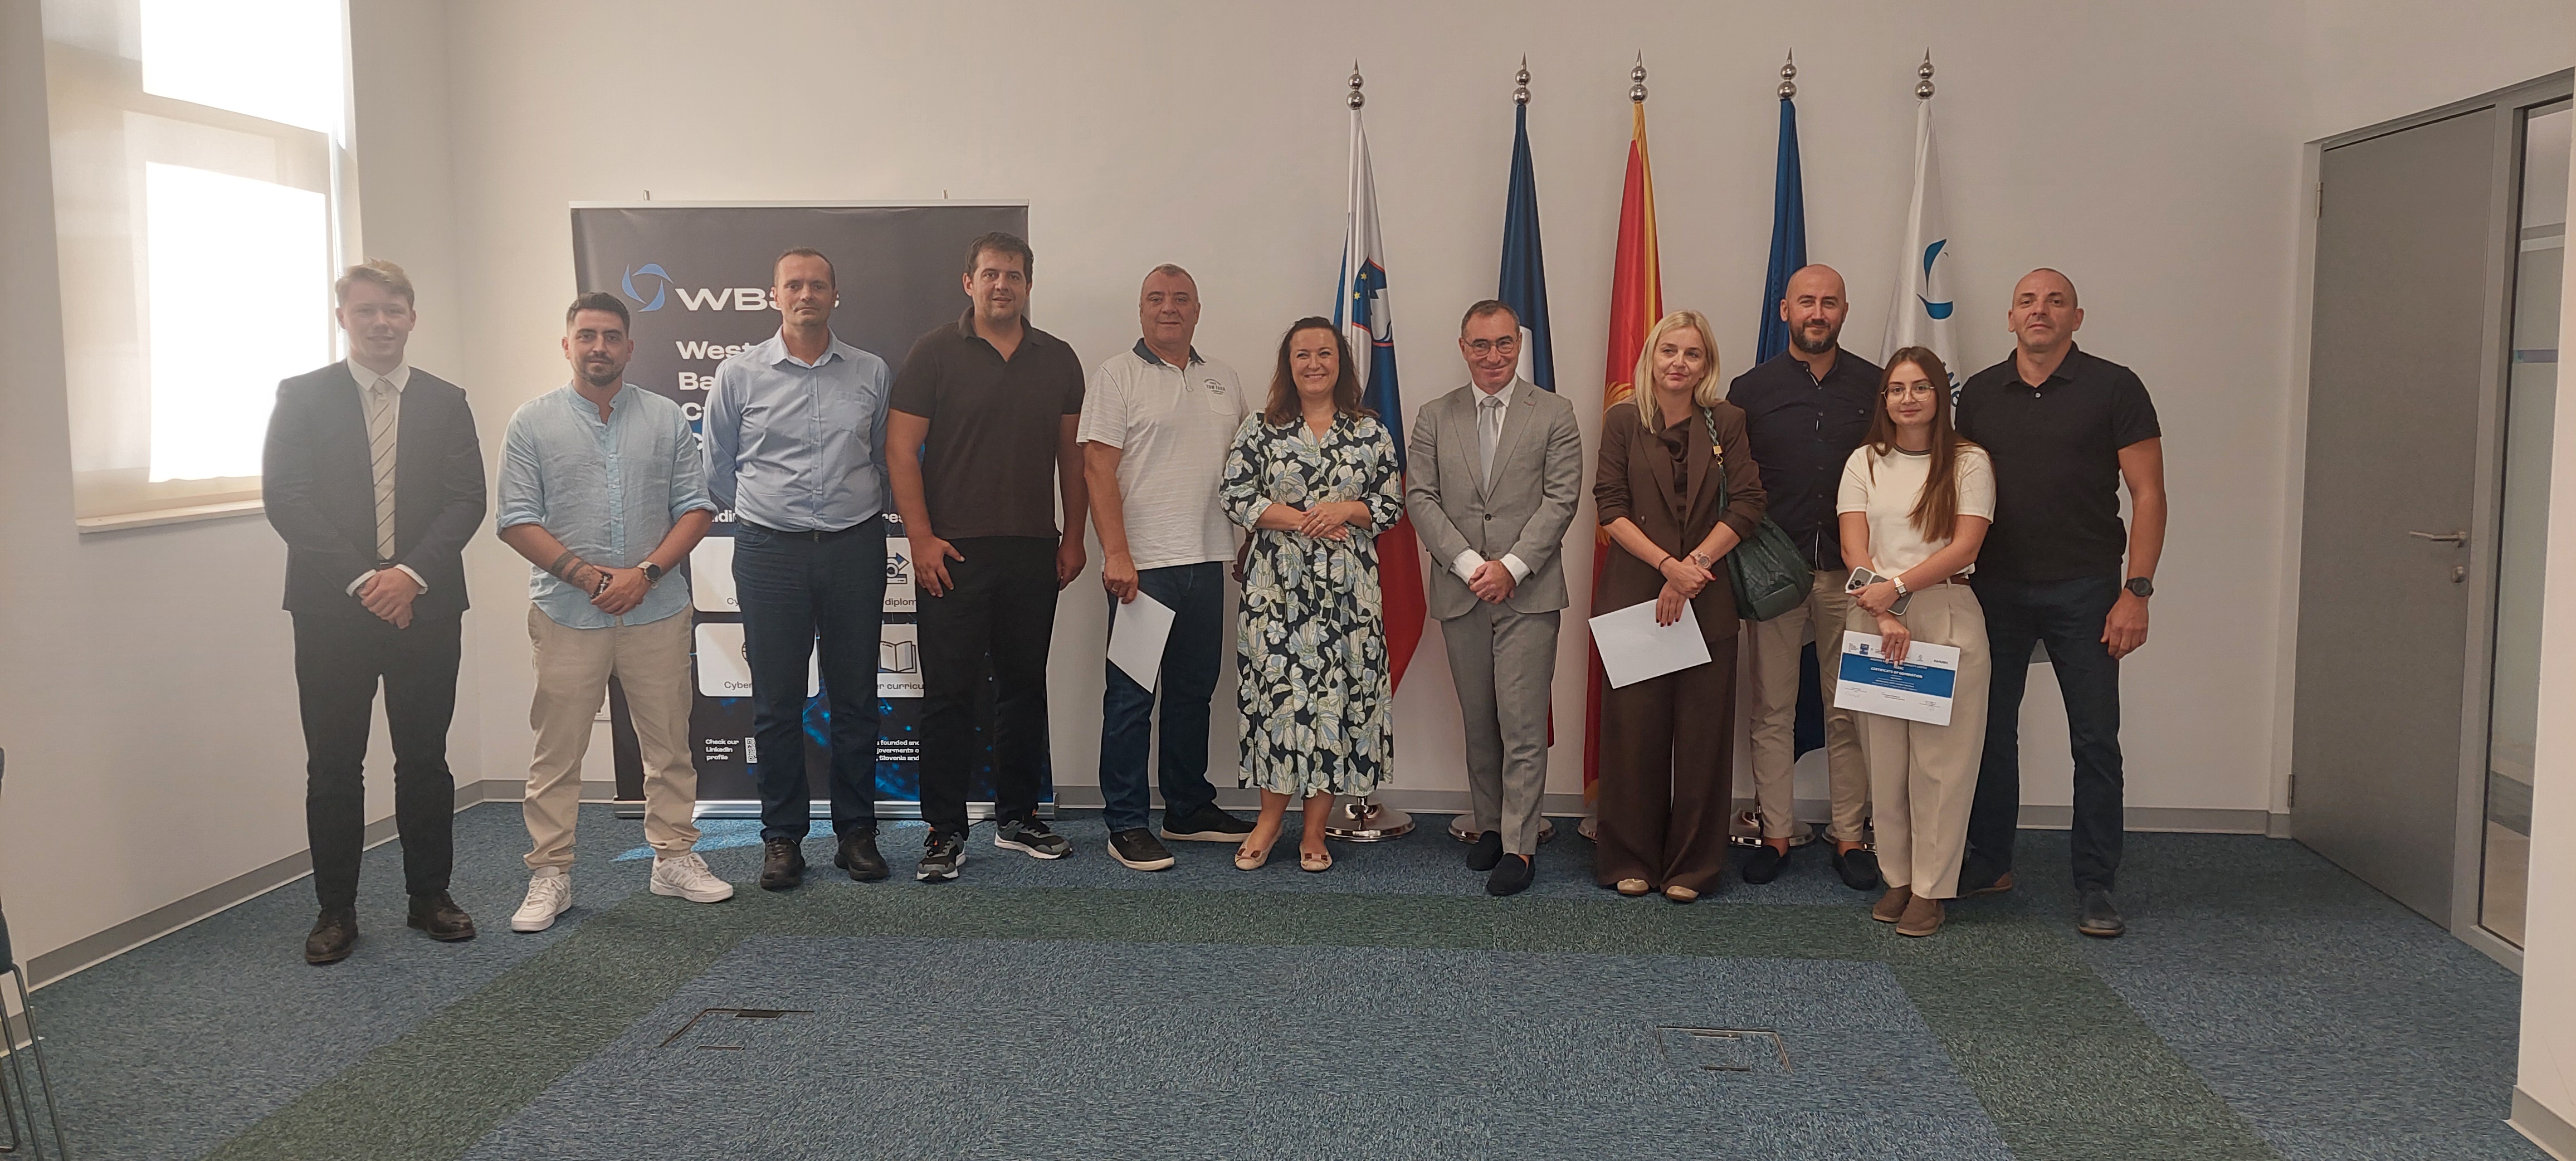
This week at WB3C, participants from public institutions across the Western Balkans are looking at the information environment from three different but closely connected perspectives: cyber awareness, disinformation and open-source intelligence (OSINT).
The training is delivered by Marcin Napiórkowski, Sylwia Adamczyk and Jakub Orzeszek from NASK – the Polish Research and Academic Computer Network, combining practical cyber hygiene with an understanding of how information is manipulated, verified and analysed online.
The first part of the course focuses on cyber awareness in both private and professional environments. Participants examine common threats from an end-user perspective, incident reporting, protection of email and social media accounts, and the security practices that organisations can put in place to reduce everyday exposure.
From there, the discussion moves to disinformation and the mechanisms that make it effective: filter bubbles, cognitive biases and techniques such as false context and cherry-picking. An important part of the work is not only recognising manipulation, but understanding how institutions can respond and communicate when misleading information begins to affect their reputation or the audiences they serve.
The OSINT component then takes participants into the practical work of finding, verifying and evaluating information from open digital sources. Search techniques, social media and visual-media analysis are combined with exercises in identifying disinformation and checking the reliability of what has been found.
There is also another side to OSINT that is sometimes overlooked: protecting the analyst. Participants are introduced to OPSEC methodologies and operational anonymity, looking at how research can be conducted without unnecessarily exposing the analyst, the organisation or the investigative workflow.
Bringing these three areas together is particularly relevant for public institutions. The same digital environment in which staff communicate and work is also the environment in which information is collected, manipulated, amplified and investigated.
By the end of the course, the objective is therefore not simply to know more tools or terminology, but to be better able to recognise threats, question information, verify sources and work more securely online.
Gilles Schwoerer, our Programme Director, greeted the participants and thanked our partners in URSIV, Urad Vlade Republike Slovenije za informacijsko varnost for funding this training and its continued support to WB3C activities.
14.09.2026
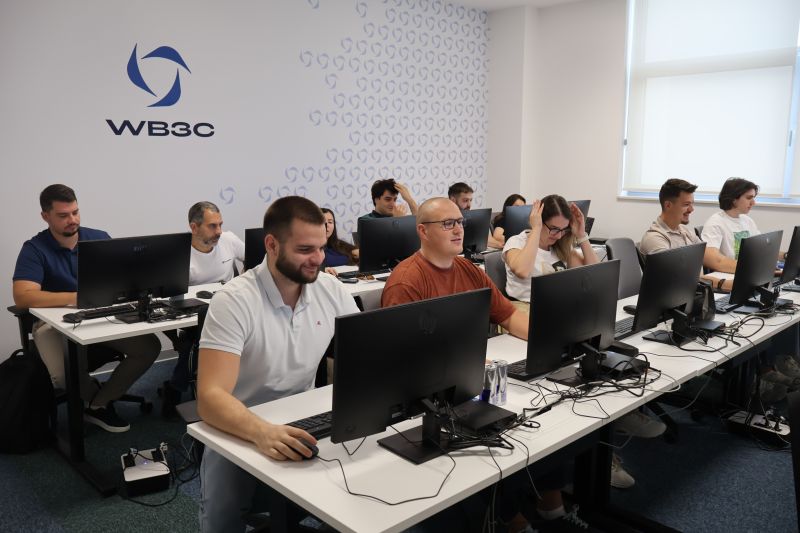
The last two-week block of the Cybersecurity Diploma Course with the French Université de Technologie de Troyes
This week, our students had the opportunity to explore digital forensics through a practical and investigation-oriented approach, combining technical knowledge, forensic tools and, most importantly, analytical reasoning.
The training was delivered by Ljuban Petrovic, Reza Elgalai and Marc TEROUANNE, digital forensics specialists, drawing on several years of operational experience in digital investigations and forensic examination.
Throughout the week, participants worked progressively from the fundamentals of digital evidence to a complete forensic investigation.
They learned about evidence preservation, integrity and hashing, before exploring key Windows forensic artefacts such as Prefetch, UserAssist, JumpLists and ShellBags. Rather than simply learning where artefacts are located, the objective was to understand the link between a user action and the digital traces left behind on a system.
The participants first generated activity themselves inside their own virtual machines, then used tools such as Eric Zimmerman's forensic tools, X-Ways Forensics and Magnet AXIOM to identify and interpret the traces they had created.
The second part of the week introduced OperationBlueHarbor, a realistic investigation scenario designed specifically for the course. From a forensic disk image, participants had to work as real analysts: explore the system, recover deleted information, identify relevant evidence, correlate artefacts and distinguish facts from assumptions.
Later in the investigation, a memory dump was introduced as a new source of evidence. Using Volatility 3, participants examined running processes, focused on Tor-related activity, extracted process memory and searched for relevant strings and indicators. Particular attention was given to one of the most important skills in digital forensics: understanding what a trace can prove — and what it cannot prove.
The week concluded with evidence correlation, reporting and discussion around how technical findings can be transformed into clear, understandable and useful information for an investigation.
The philosophy throughout the course was simple:
Digital forensics is not about clicking buttons in a forensic tool. It is about understanding the traces, questioning the results, correlating the evidence and being able to explain your conclusions.
A demanding but very rewarding week, with an engaged group of participants who progressively moved from following demonstrations to conducting their own investigation.
Congratulations to everyone who took part in the course for their dedication throughout the intensive 10 week training — especially for surviving Operation Blue Harbor! What comes next are the final exams, the dissertation defence and the internationally recognised university diploma.
10.09.2026
OSINT and the dark web: supporting anti-drug investigations
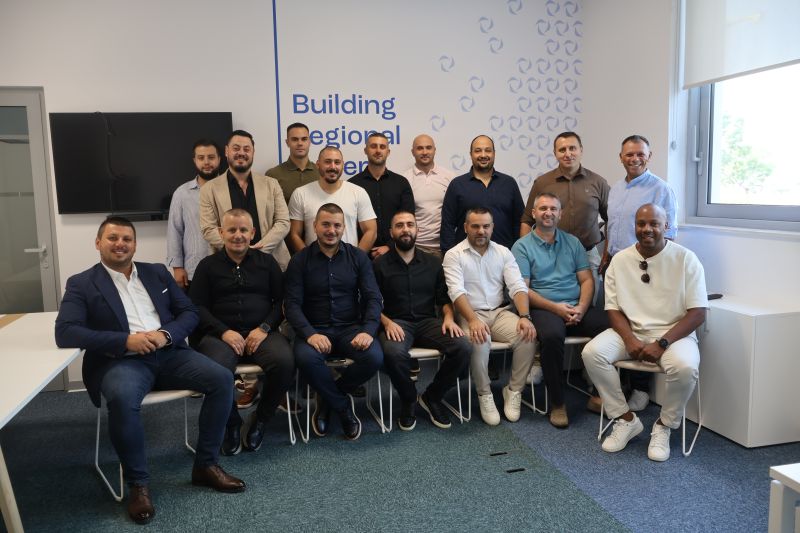
This week at WB3C, we concluded a four-day OSINT – Dark Web training for anti-drug police units, coming from law enforcement units from across the Western Balkans. The course was designed for police officers working in drug units and joining a WB3C training for the first time.
The focus was practical: how publicly available information can support internet-based investigations, from identifying potential threats and collecting digital evidence to producing actionable intelligence for operational decision-making.
Over four days, participants worked through the fundamentals of OSINT, evidence preservation, online protection and anonymisation, social-network investigations, investigative checks, the dark web, and structured data-collection planning. Particular attention was given to preserving the integrity of digital evidence and navigating online environments safely and securely.
The training was delivered by Nicholas Michee from OFAST, France, together with Cyril CORRIAS, WB3C’s cybercrime trainer. Combining specialist anti-drug investigation experience with cybercrime expertise, they guided participants through the technical and investigative aspects of using open-source information and online environments in support of operational work.
Thank you to Nicholas Michee and our partners at OFAST, France, for their cooperation and expertise, and to Cyril Corrias for his contribution to the training. Thank you also to the participating officers for four days of focused practical work and professional exchange.
09.09.2026
“We just got hacked!”
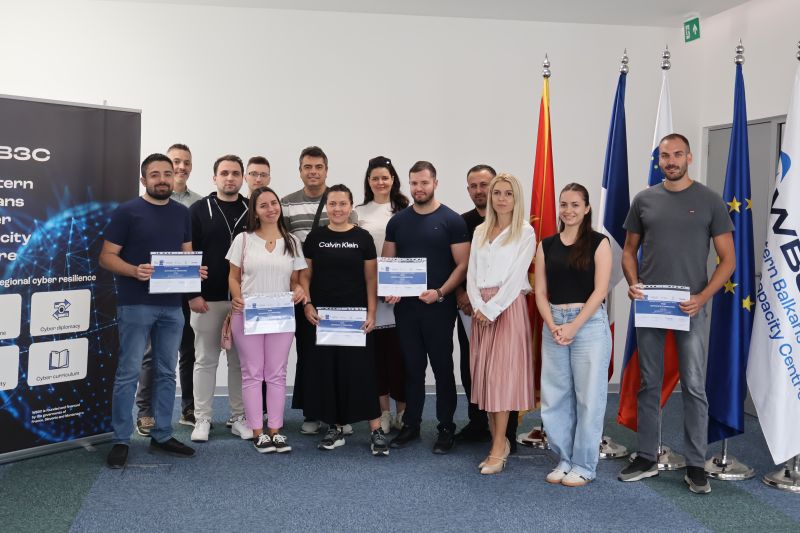
Yesterday, we wrapped up “We just got hacked”, a basic three-day technical training on incident response for entry level system administrators and cybersecurity specialists from regional public institutions to work through what happens after a security alert becomes a real incident: how to triage it, identify what matters first, analyse logs, trace the likely attack vector and examine suspicious files for indicators of compromise.
Participants worked with the MITRE ATT&CK framework, connecting investigative findings with attacker tactics and techniques, and looking at how those findings can be translated into practical hardening and preventive measures. The objective was not simply to understand how an incident happened, but to use that analysis to reduce the organisation’s exposure to similar attacks in the future.
The training was delivered by Jakub Bajera and Krzysztof Chudzik from NASK – Naukowa i Akademicka Sieć Komputerowa / Research and Academic Computer Network, Poland. We also thank our funding partners at URSIV, Urad Vlade Republike Slovenije za informacijsko varnost for their continued support to WB3C and to the development of cybersecurity capacities across the Western Balkans.
Certificates are awarded by Jean-Pierre Bonnet, JP BNT, our new WB3C colleague working across cybercrime and cybersecurity.
08.09.2026
WB3C meets critical infrastrucutre operators in Prishtina
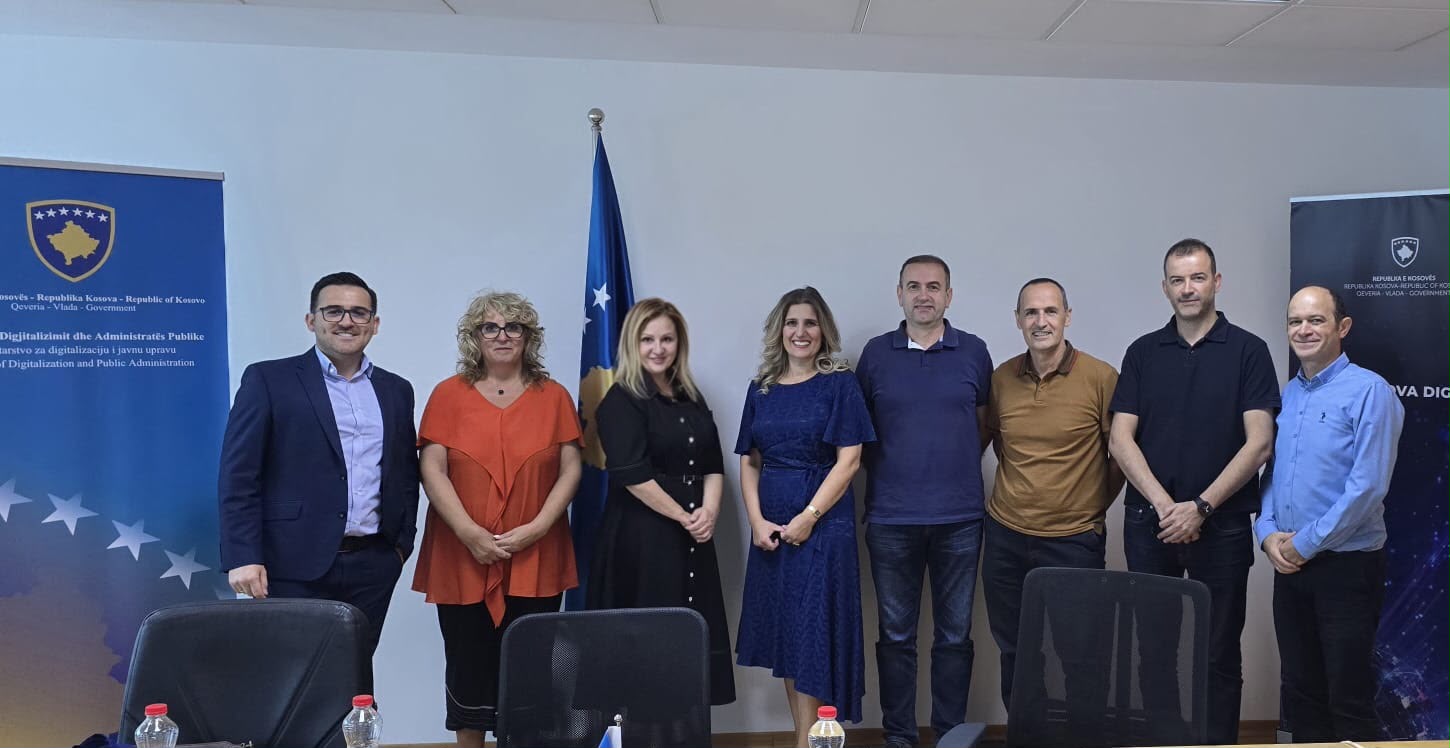
During a recent mission to Prishtina, WB3C joined CIVIPOL colleagues working on a Gap and Needs Assessment related to the protection of critical infrastructure and public spaces.
While the CIVIPOL assessment focused particularly on the institutional and legislative framework, including the role of the Ministry of Interior and alignment with the EU Critical Entities Resilience (CER) Directive, WB3C used the opportunity to engage directly with critical infrastructure operators and better understand their operational needs.
Together with Shkumbin Saneja from the Ministry of Digitalisation and Public Administration, WB3C met representatives from several key sectors: Arijeta Pajaziti Qerimi and Uran Thaci from energy, Adelina Dumani-Hulaj from Prishtina International Airport, Gazmend Gashi from transport/aviation, Arianit Maraj from telecommunications and Arbnor Imeri from the banking sector.
The discussion provided a useful cross-sector view of existing gaps, operational needs and capacity-building priorities. Despite the differences between sectors, a number of common areas of interest emerged.
This forms part of a wider regional process. WB3C will continue meeting key critical infrastructure stakeholders across the Western Balkans to better understand both sector-specific and shared needs, and to use these findings to shape a training and capacity-building plan tailored to the realities operators are facing.
This work is being carried forward in synergy with our partners under the EU-funded CEPS project, linking institutional assessments with the operational perspective of those responsible for running and protecting critical services.
07.09.2026
WB3C and CIVIPOL Assess Critical Infrastructure Protection Needs Across the Western Balkans
WB3C, in cooperation with its French partner CIVIPOL, launched a series of country missions across the Western Balkans to assess the capacity-building needs of institutions and operators responsible for critical infrastructure and essential services.The initiative aims to identify existing capabilities, operational challenges and priority areas for improvement, particularly in the context of growing cyber threats and the region's alignment with the EU's Critical Entities Resilience (CER) and NIS2 Directives. The missions began in Prishtina on 7 September, where representatives of relevant public institutions and critical infrastructure operators discussed their responsibilities, preparedness and training needs. The regional assessment subsequently continued over September and October with consultations in other Western Balkan administrations, including visits to Tirana, Skopje, Podgorica, Belgrade and Sarajevo.
The findings will help WB3C and its partners develop more targeted capacity-building programmes, addressing the specific needs of critical entities while identifying shared challenges that could benefit from regional training and cooperation.
By linking needs assessments directly to future training, WB3C aims to move towards a more tailored, demand-driven approach to strengthening critical infrastructure resilience across the Western Balkans.
Photo by: Magnific
04.09.2026
WB3C welcomes Jean-Pierre Bonnet to its team
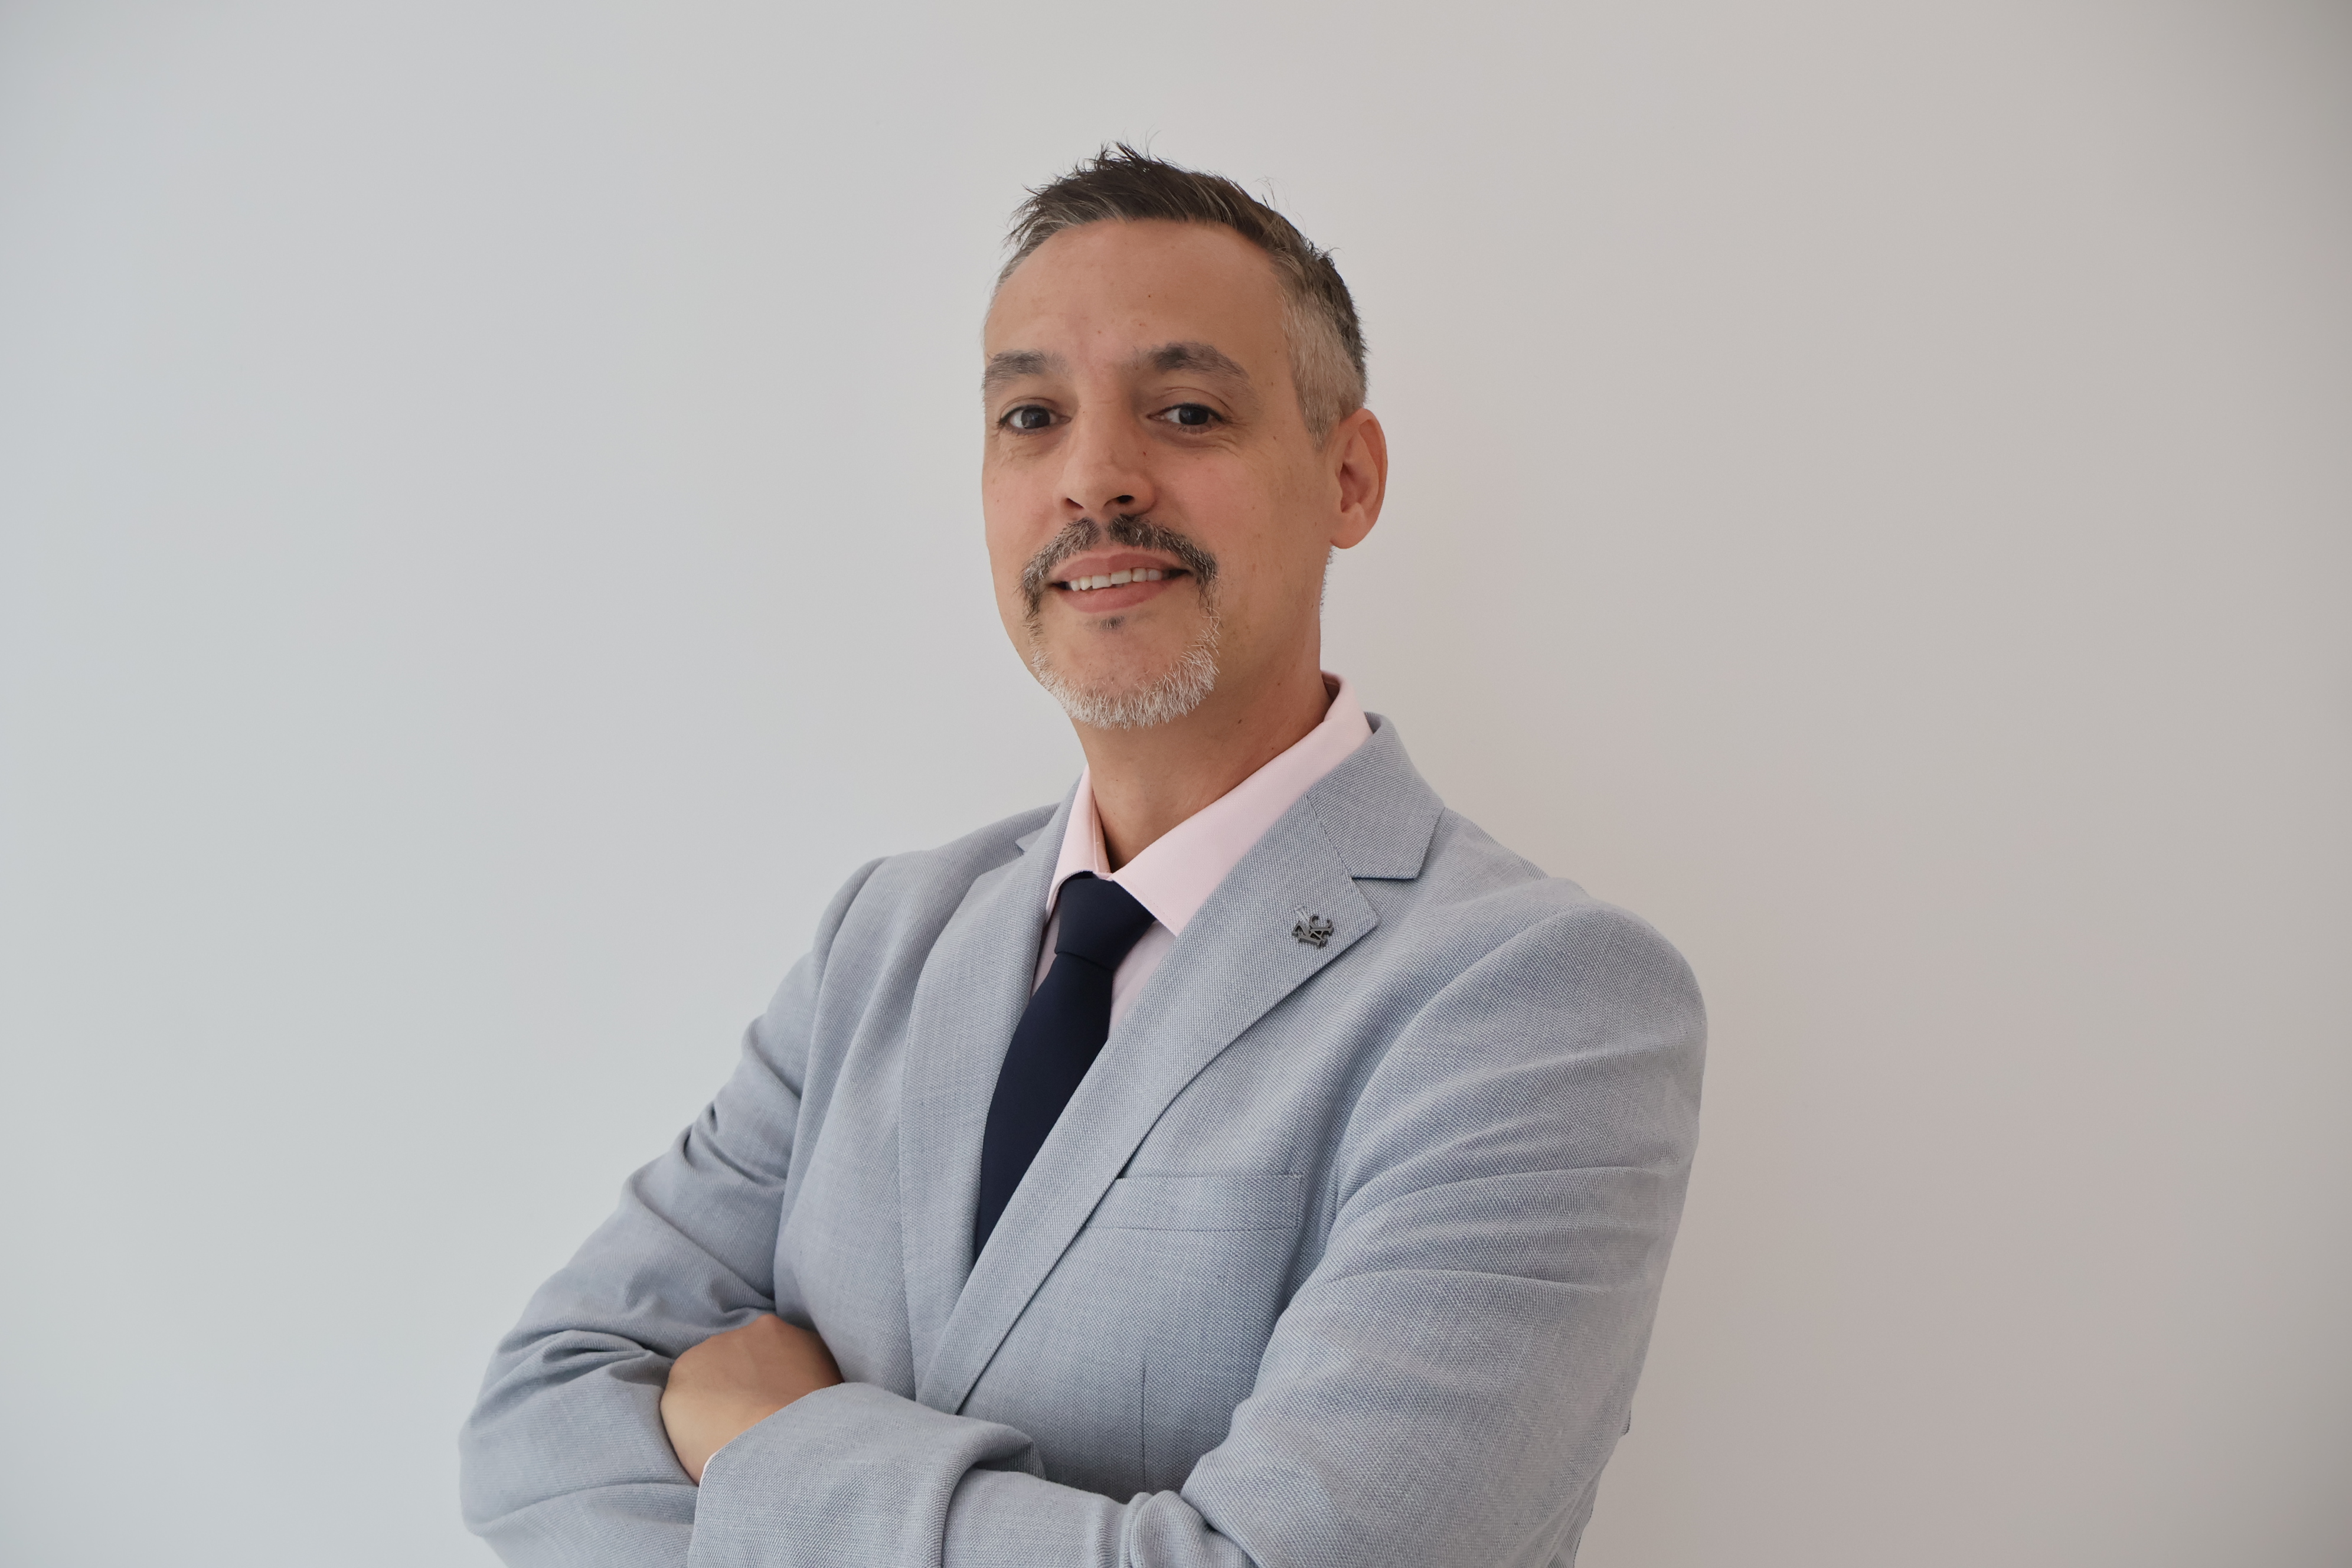
We are pleased to welcome Jean-Pierre Bonnet, who joins the Western Balkans Cyber Capacity Centre (WB3C) as a trainer working primarily in the field of cybercrime, while also contributing to the Centre’s cybersecurity activities.
Jean-Pierre began his career in the French Gendarmerie, initially serving in a mobile unit responsible for public-order operations and overseas deployments. He later moved into criminal investigations, progressively specialising in cybercrime-related fields and, in his most recent assignment, working on complex investigations across France.
His professional experience includes open-source intelligence (OSINT), digital forensics and Internet investigations, alongside training and knowledge-sharing with partner administrations in France. He is also completing a long-term professional training programme in cybersecurity and governance, further broadening the expertise he brings to WB3C.
At the Centre, Jean-Pierre will work with partners across the Western Balkans to support the development of skills and operational knowledge in cybercrime, while contributing with the wider team to the continued development of WB3C’s activities.
Welcome to the team, Jean-Pierre!
30.06.2026
Visit by CBRN Centres of Excellence Project 101
WB3C was pleased to meet with representatives of the EU CBRN Centres of Excellence Project 101 to discuss potential cooperation in strengthening critical infrastructure protection and security.
The exchange with Alexandre Custaud, EU CBRN CoE Project 101 Team Leader and Scott S. focused on possible synergies between cybersecurity, CBRN risk mitigation and broader critical infrastructure resilience. As threats to essential services become increasingly interconnected, cross-sector cooperation is essential to support more coordinated, practical, and future-oriented capacity building.
WB3C team Gilles Schwoerer and Maja Miranovic stressed that sectoral approach in building resilience for critical infrastructure is central in our 3-year EU funded programme and expressed readiness to explore areas where our respective expertise and regional engagement can contribute to stronger resilience and security.


